Cursor Traces Security Breach to Exposed Access Key
According to reporting from Unite.ai, the AI code editor Cursor has traced a recent security breach back to an access key that was inadvertently exposed by Fireworks AI. Security incidents involving third party integrations continue to highlight potential vulnerabilities across interconnected artificial intelligence software supply chains and development environments.
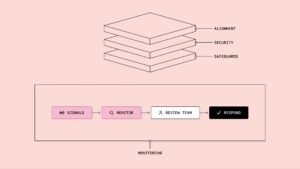
As development teams increasingly adopt specialized AI tools and infrastructure platforms, managing credentials securely remains a critical challenge. The exposure underscores the importance of rigorous access controls and continuous monitoring for third party services that handle sensitive API keys and authentication tokens. Further details regarding the exact scope of the exposed data and the remediation steps taken by both companies were detailed in the original report by Unite.ai.
Based on reporting by www.unite.ai.